Source & artifact analysis
Android, iOS, packaged metadata, and traceable findings.
Application security & engineering intelligence
From the code you write to the application you ship. Explore security findings, release policy, and Android runtime protection with AppArmorX.
Early product stage · Mobile-first foundations
A hands-on look
Choose a finding. Inspect its evidence. Change a policy threshold and see how the review changes.
Sample findings ready
NSAllowsArbitraryLoads = trueThe sample stays visible while the threshold changes.
Choose your starting point
Analysis platform
Review Android and iOS source, configuration, dependencies, and APK/IPA metadata. Bring findings into a shared policy and reporting model.
Android runtime engine
Gradle-delivered lifecycle guards, native probes, and a firewall for supported dependency calls. Evaluate the engine on the devices you ship for.
Inside the Android engine
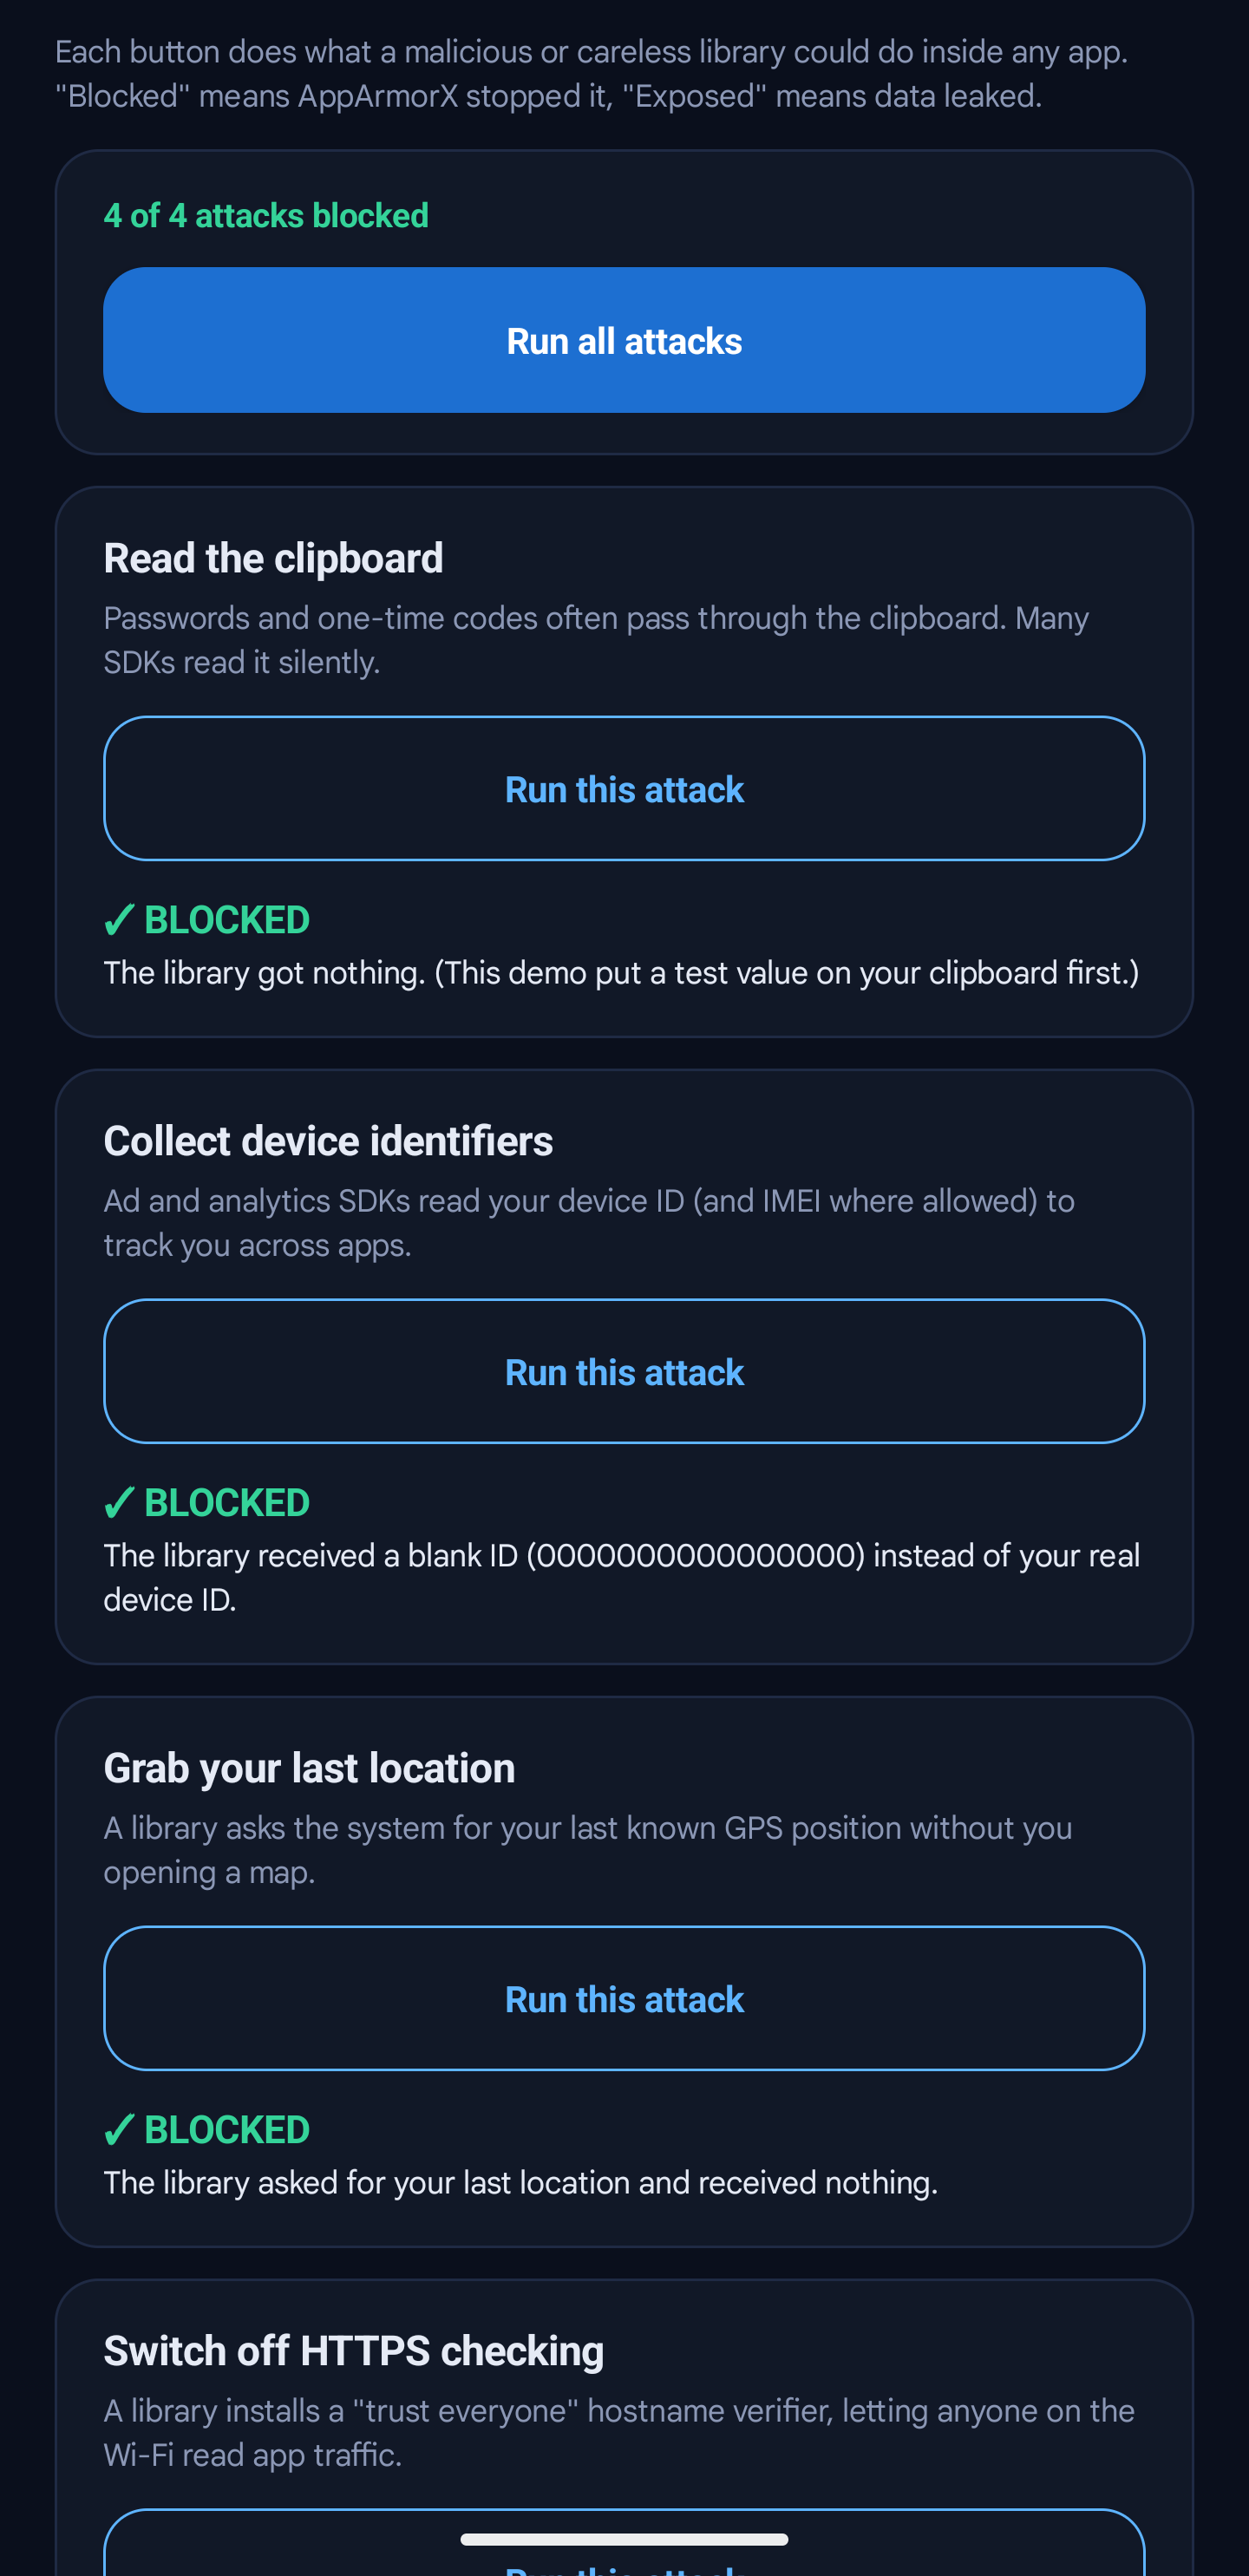
The sample app exposes individual checks and supported attack scenarios. Unknown outcomes stay unknown. Detection and prevention remain separate claims.
Recorded sample, not a live device session. The engine is pre-release and has documented bypass and timing limits.
Built to go deeper
AppArmorX's core is deterministic. Structured evidence supports policy, reporting, and evolving engineering context. AI interpretation is a separate development direction.
Understand the platform ↗Android, iOS, packaged metadata, and traceable findings.
JSON, SARIF, baselines, and visible suppressions.
Topology and dependency health with deeper context to follow.
Let's build from a real problem
Talk directly with Shushant Tiwari about evaluation, runtime protection, or a workflow that needs better evidence.